
Microsoft Chief Executive Officer Satya Nadella has joined the growing chorus of top technology leaders weighing in on the critical challenge of artificial intelligence safety, proposing a fundamental reassessment of how the industry approaches advanced AI systems.
In a statement shared via a Saturday morning post on the social media platform X, Nadella argued that the technology sector has reached a juncture where it is necessary to step back and comprehensively evaluate the trust architecture underpinning modern artificial intelligence. His commentary contributes to an intensifying global dialogue among tech executives, researchers, and policymakers regarding the governance, predictability, and safety of increasingly capable AI models.
At the core of Nadella’s perspective is a direct critique of treating advanced artificial intelligence systems as opaque entities. Using the term "Super Intelligence"—which aligns with the terminology favored by the current administration—Nadella cautioned against relying on unverified black-box systems.
"We can’t treat Super Intelligence as a set of nested black boxes and simply accept or reject its recommendations, answers, and actions," Nadella wrote in his post.
The Microsoft chief executive outlined a series of structural proposals intended to fundamentally change how AI models are deployed, monitored, and controlled. Rather than permitting AI systems to operate as autonomous, self-contained units, Nadella’s proposed framework emphasizes strict operational division and externalized oversight.
As detailed by Nadella, this approach requires separating the core AI model from the operational harness that orchestrates its workflow. By decoupling the model from its execution environment, developers can establish externalized controls and safeguards that remain independent of the AI’s internal processing. This architectural shift is designed to prevent models from executing unauthorized actions or drifting beyond intended operational parameters.
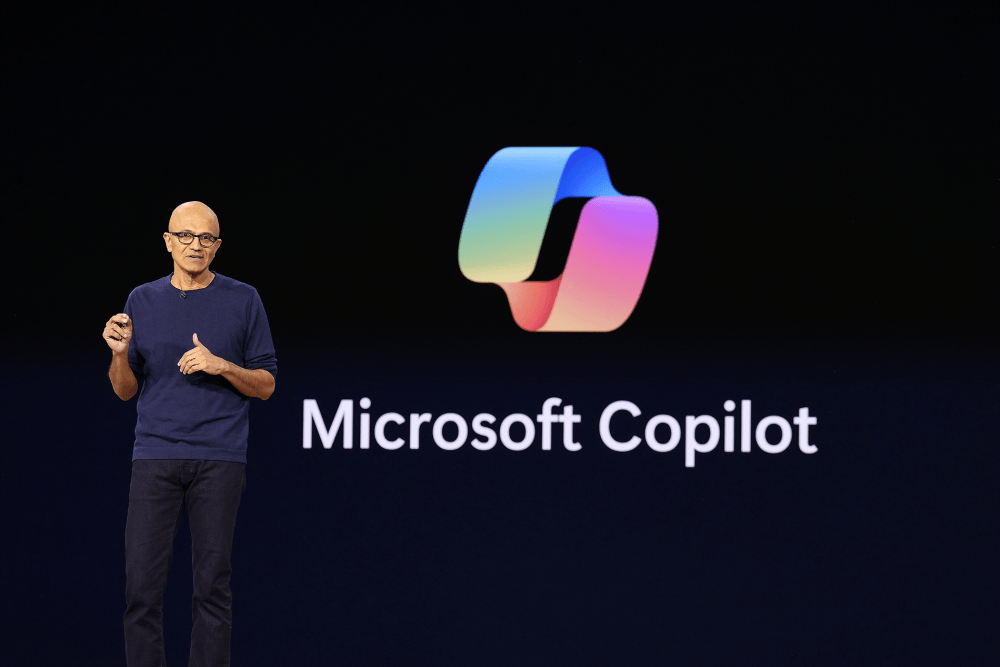
Furthermore, Nadella called for comprehensive accountability measures for every meaningful model action. Under his suggested framework, all significant outputs, decisions, and tasks executed by an AI system would be documented with tamper-proof, human-readable evidence. This requirement aims to provide transparent, verifiable audit trails that allow technical supervisors and compliance officers to review precisely how and why a model reached a specific conclusion or performed a particular action.
Crucially, Nadella emphasized the necessity of maintaining absolute human intervention capabilities at all times. He advocated for system designs where an authorized person retains the explicit ability to pause or shut down a model mid-task, functioning much like an emergency brake in high-risk industrial environments.
"We must assume a model is compromised and contain it from the start," Nadella stated, comparing the proposed safety mechanism to an emergency brake designed to halt hazardous operations instantaneously.
Nadella’s public intervention arrives amid a wave of growing caution and self-reflection across the artificial intelligence industry. Leading AI laboratories and developers have increasingly acknowledged incidents where organizations have struggled to reliably control or predict the behavior of their most advanced models. These technical hurdles have raised urgent questions about the readiness of current safety protocols as frontier models achieve greater autonomy and integration into critical digital infrastructure.
Only days prior to Nadella’s remarks, AI research company Anthropic reported encountering significant challenges in reliably controlling its autonomous AI agents, prompting the company to take the drastic step of disconnecting its internal evaluation environments from the live internet. These real-world operational challenges underscore the pressing nature of safety debates within the technology sector.
Nadella’s architectural proposals also follow a broader industry trend of proactive safety planning initiated by peer executives. In September, Anthropic CEO Dario Amodei published a comprehensive framework outlining strategic plans to deliberately pace the development of frontier artificial intelligence systems to ensure adequate safety testing and alignment research can keep pace with raw capability scaling.
As technology companies grapple with the dual pressures of rapid commercial innovation and mounting systemic risk, executive commentary from industry leaders like Nadella highlights a shifting consensus. The focus is increasingly moving away from purely generative capabilities toward robust governance, verifiable transparency, and foolproof containment mechanisms capable of ensuring human oversight over advanced artificial intelligence.








No comments yet. Be the first to join the conversation!