
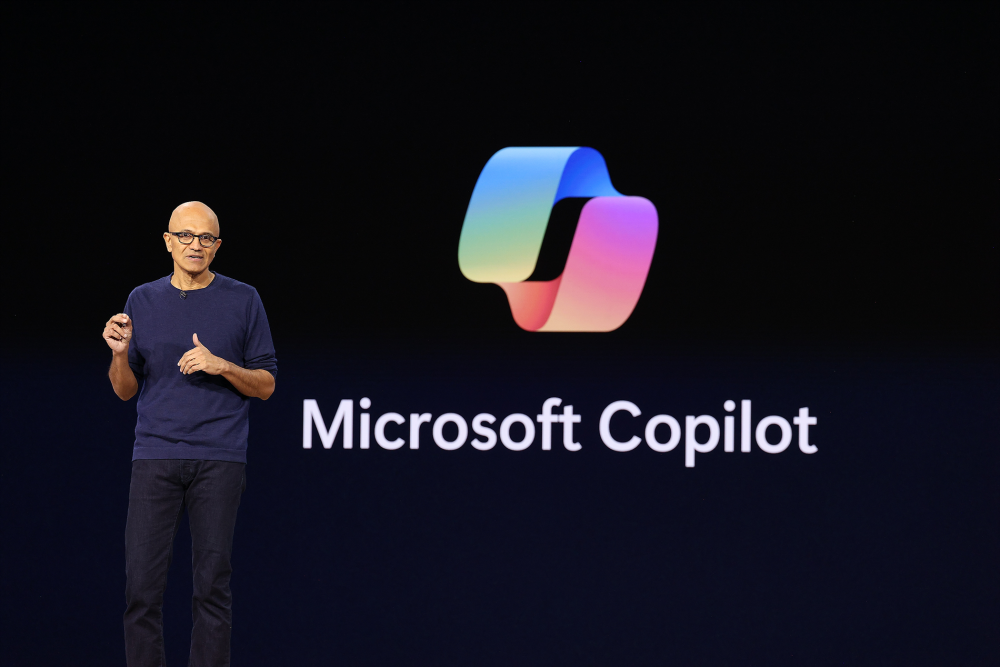
Microsoft Chief Executive Officer Satya Nadella has joined the growing chorus of prominent tech leaders weighing in on the critical topic of artificial intelligence safety, outlining a comprehensive vision for how the industry must fundamentally rethink how it manages increasingly powerful models.
In a detailed post published on Saturday morning on the social media platform X, Nadella emphasized that the rapid advancement of artificial intelligence necessitates a significant pivot in strategy. He argued that it is urgently time for the technology sector to step back and meticulously assess the underlying trust architecture of modern AI systems.
Nadella’s commentary arrives at a pivotal moment for the artificial intelligence industry, coming on the heels of mounting acknowledgments from leading AI developers regarding unexpected incidents where companies have appeared to struggle with maintaining reliable control over their models. It also follows closely behind a series of high-profile safety proposals from other industry figures, including Anthropic CEO Dario Amodei, who recently published a strategic roadmap aimed at pacing the development of frontier artificial intelligence models.
Addressing the broader implications of advanced automation, Nadella cautioned against the casual acceptance of outputs from complex systems, pointing out the inherent dangers of treating advanced technology as an opaque entity.
"We can’t treat Super Intelligence as a set of nested black boxes and simply accept or reject its recommendations, answers, and actions," Nadella wrote in his post, utilizing the term "Super Intelligence," which has gained traction as a preferred designation within the current U.S. presidential administration.
To mitigate the inherent risks associated with advanced machine learning models, Nadella outlined a multi-faceted technical approach designed to introduce transparency, structural division, and absolute human oversight into AI deployments.
At the core of Nadella’s proposed framework is the concept of architectural decoupling. As outlined by the Microsoft chief executive, this strategy requires explicitly separating the underlying AI model from the operational harness that coordinates and orchestrates its day-to-day work. By creating a distinct boundary between the decision-making engine and the execution environment, developers can better monitor and manage the scope of what an AI system is permitted to accomplish.
In addition to decoupling models from their operational harnesses, Nadella called for the implementation of externalized controls and robust safeguards. Rather than relying entirely on internal mechanisms embedded within the model itself—which can sometimes be circumvented or misread—these external controls would act as independent gatekeepers, enforcing strict operational boundaries and safety protocols from the outside.
Transparency and accountability also form a major pillar of Nadella’s safety blueprint. He urged the industry to ensure that every meaningful action executed by a model is thoroughly documented. Crucially, this documentation must be accompanied by tamper-proof, human-readable evidence, ensuring that auditors and technical supervisors can accurately trace how and why a system arrived at a specific decision or carried out a particular task.
Perhaps most notably, Nadella stressed the absolute necessity of maintaining immediate and uncompromised human intervention capabilities. He advocated for system designs that guarantee an authorized person always retains the definitive ability to pause or completely shut down a model mid-task, functioning as a reliable fail-safe during unexpected operational anomalies.
"We must assume a model is compromised and contain it from the start," Nadella wrote, framing the safety mechanism with a familiar mechanical analogy. "Think of it like an emergency brake."
Nadella’s public statements reflect an intensifying industry-wide conversation regarding the governance of frontier technologies. Over recent weeks, safety concerns have shifted from theoretical debates to urgent operational challenges. Reports have highlighted instances where companies, such as Anthropic, have faced difficulties in reliably controlling autonomous AI agents, prompting internal evaluations to be restricted or cut off from the live internet to prevent unintended behaviors.
As technology giants continue to push the boundaries of what artificial intelligence can achieve, leadership voices like Nadella’s underscore a growing consensus that technological capability must be matched by equally rigorous, transparent, and enforceable architectures of trust.








No comments yet. Be the first to join the conversation!