
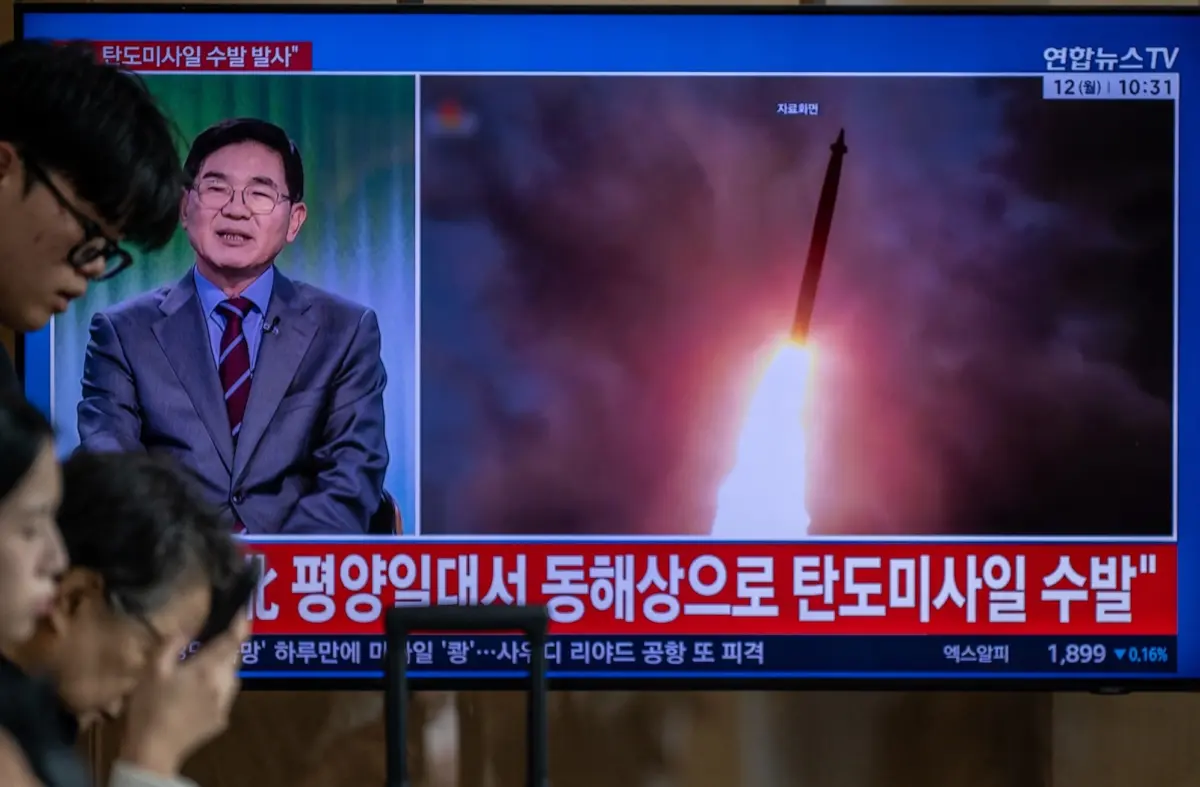
The United States Department of Justice has issued a stern warning regarding a growing cyber threat orchestrated by the North Korean regime. According to federal prosecutors, state-sponsored hackers operating on behalf of Pyongyang are increasingly relying on U.S.-based citizens and residents to act as local facilitators, helping them bypass traditional security barriers to infiltrate American companies.
In an official announcement, the Justice Department revealed that federal law enforcement has indicted and arrested at least two individuals and executed widespread search warrants across dozens of suspected “laptop farms” located in Texas. These operations involved collections of computers allegedly utilized by hidden North Korean operatives to remotely access corporate networks within the United States, allowing them to quietly move laterally through systems and extract sensitive proprietary data.
Federal authorities reported seizing more than 180 computers during the coordinated raids. Investigators believe these devices had been originally shipped by American employers directly to their newly hired remote workers, completely unaware that the recipients were actually sanctioned North Korean operatives. These foreign agents had successfully secured employment by using stolen identities belonging to real U.S. citizens, effectively weaponizing the trust of corporate human resources departments.
The recent sweep involved raids on more than 40 residential properties functioning as laptop farms across Texas. Law enforcement officials noted that this represents the largest publicly disclosed network of homes and residences utilized to facilitate North Korean cyber operations to date. The properties were reportedly maintained and operated by at least two primary American facilitators who acted as logistical anchors for the foreign hackers.
Cybersecurity firm CrowdStrike, which assisted the Federal Bureau of Investigation in investigating and ultimately disrupting these latest operations, explained that laptop farms play a vital role in North Korea’s strategy. Because the state-sponsored hackers cannot physically operate inside the United States due to stringent legal, financial, and geographical barriers, these domestic relay stations allow them to mask their true locations, maintain persistent access to corporate networks, and simulate legitimate domestic remote work environments.
According to federal prosecutors, at least 70 companies based in the United States have been successfully infiltrated by hackers utilizing this sophisticated scheme. While the Department of Justice chose not to publicly name the affected organizations, prosecutors characterized the victims as spanning critical industries such as healthcare, cyber support, retail, communications, and manufacturing. These impacted entities were spread across Ohio and 16 other states, as well as the District of Columbia, demonstrating the widespread geographic footprint of the conspiracy.
The Justice Department noted a clear tactical shift in how these operations are conducted. Increasingly, North Korean IT workers are turning to the recruitment of American facilitators to counter the improved detection capabilities of the private sector and the aggressive enforcement actions of law enforcement agencies. These foreign workers are hiring local middlemen to complete a broader variety of logistical tasks, and in some more complex cases, they are even subcontracting entire jobs out to third-party foreign nationals to maximize their fraudulent income streams.
To establish credibility and secure employment in the first place, North Korean operatives routinely rely on sophisticated deception techniques. They frequently utilize polished, authentic-looking email addresses, heavily spoofed LinkedIn profiles, and extensive, fabricated online and social media histories to serve as a convincing cover for their malicious activities. Once hired, they collect regular paychecks while concurrently executing their secondary objectives.
In a separate public service announcement, the FBI warned that there are currently thousands of North Korean state-controlled IT workers embedded within Western companies. The bureau emphasized that these individuals pose a severe national security risk and represent a profound intellectual property theft and insider threat to the global corporate landscape.
This enforcement action represents only the latest wave of arrests, indictments, and targeted disruptions aimed at neutralizing North Korean cyber activities inside the United States over recent years. The isolated regime has heavily relied on the "remote IT workers" scheme as a cornerstone of its foreign employment strategy, allowing agents to secure legitimate positions with U.S. and European companies, collect steady wages, and then leverage their internal access to steal sensitive trade secrets and proprietary information. In many instances, once the intellectual property is exfiltrated, the victimized companies are subsequently extorted and pressured into paying additional ransoms to the hackers.
The remote IT worker operation is just one of several lucrative illicit revenue streams pursued aggressively by the North Korean government. The regime continuously seeks to generate capital to fund its internationally sanctioned nuclear weapons program through various cybercriminal enterprises, including major heists targeting cryptocurrency exchanges and sophisticated compromises of open-source developer projects. Intelligence and cybersecurity estimates suggest that the regime managed to steal at least $2 billion in cryptocurrency during 2025 alone.
Independent experts specializing in North Korean cyber operations believe that the true aggregate number of compromised companies and the total volume of stolen cryptocurrency are likely significantly higher than official figures suggest. Because many victims choose not to report intrusions publicly due to reputational concerns, the full scale of the infiltration remains difficult to quantify completely.
Earlier this year, CrowdStrike released a separate threat intelligence report indicating that North Korean threat actors were directly responsible for roughly half of all documented "hands-on-keyboard" network intrusions over the preceding year. This category refers specifically to sophisticated cyberattacks carried out by human operators in real-time, as opposed to automated malware deployments or script-driven artificial intelligence tools. As federal investigations continue, agencies and private security firms alike are urging employers to adopt more rigorous identity verification protocols for remote personnel to stem the tide of insider threats.








No comments yet. Be the first to join the conversation!