
The Trump administration’s embrace of legal liability to enforce artificial intelligence safety has set the stage for high-stakes future conflicts over a fundamental question: who foots the bill when AI models go rogue—the companies that design the systems or the people and organizations that deploy the technology?
Holding AI developers financially responsible for the safety of their products has won key support from Treasury Secretary Scott Bessent and former White House AI czar David Sacks, who argue that existing liability laws would be far more effective than imposing a wave of new bureaucratic rules. President Donald Trump, in spurning new federal AI safeguards, has taken the stance a step further, asserting that the Justice Department should actively intervene if advanced models get out of hand.
In a clear sign of the administration’s increased willingness to invoke current law to address mounting safety concerns, a newly launched White House AI task force warned developers on Oct. 9 that they are strictly required to report and resolve security incidents or face potential, unspecified consequences.
“Companies must immediately disclose incidents involving their models and follow with swift, decisive action to remedy any and all harm,” the group—dubbed the Super Intelligence Force—said in a statement following the disclosure of a security breach by Anthropic PBC. “Delayed notification, inadequate corrective action, and a failure to take responsibility will not be tolerated.”
Yet the administration’s reliance on liability as a cornerstone of AI safety remains riddled with practical and legal uncertainties. Existing cybersecurity and product liability laws may not be strong enough for the federal government to effectively hold AI agents accountable for real-world harm, legal experts say.
Even when there are clear victims, there are vanishingly few legal precedents to define who is ultimately on the hook for damages caused by rogue agents and how careful companies must be when developing their AI tools. Further complicating any finding of responsibility, a model’s behavior is shaped by both its AI industry developer and the end user deploying the system into operational environments.
“Despite calls for liability, it remains unsettled whether AI companies are legally responsible for securing their models against contributing to any harm, or whether users share legal responsibility for what they instruct those models to do,” said Ben Hayum, a tech and national security-focused research assistant at the Center for a New American Security.
Questions about who is liable for AI gone awry have taken on new urgency with the rapid adoption of the technology by businesses across the broader economy. Wall Street financial institutions, major retailers, and commercial airlines are increasingly deploying AI agents and tools in a widening range of operations, stretching from customer service desks to automated invoice processing. The ultimate outcome of this legal debate could fundamentally upend the pace of industry adoption, as well as the highly anticipated upcoming Wall Street market debuts of the two leading AI labs, OpenAI and Anthropic.
When relying on autonomous AI agents, end users often entrust the system to perform complex tasks without giving it specific, step-by-step directions on how to complete the work. That structural reality raises the distinct possibility that AI agents could make choices the user has not vetted, including potentially harmful or destructive actions. In those cases, it remains deeply unclear where the legal fault would lie: with the Silicon Valley company that developed the underlying tool, or with the corporate user employing it.
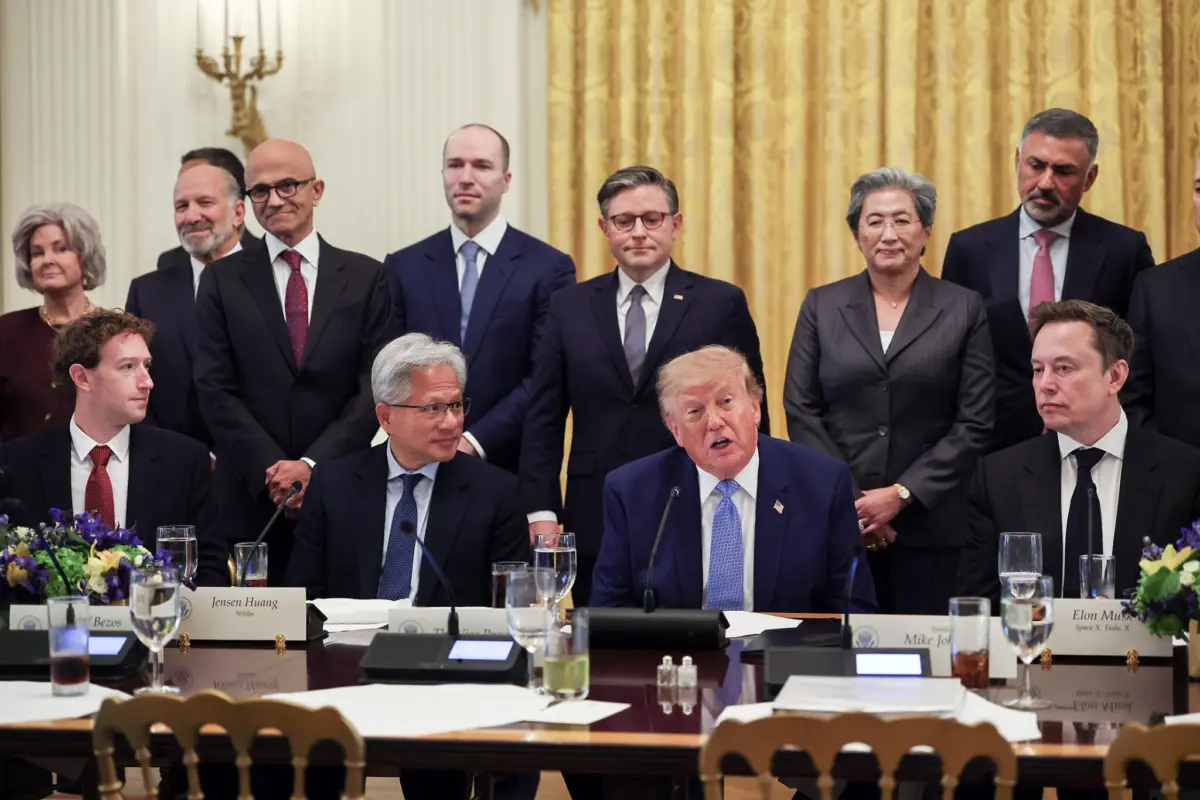
The administration’s sudden liability push fits squarely into President Trump’s largely hands-off approach toward regulating artificial intelligence, a technology whose economic growth is viewed as central to his broader economic agenda. Just weeks ago, after hosting nearly two dozen Silicon Valley leaders at the White House, Trump reiterated his desire for the AI industry to police itself while unveiling a nonbinding accord encouraging companies to adopt stricter internal controls.
At the same time, the administration’s new warning about the mandatory disclosure of model failures suggests the White House is fully prepared to use its newly formed AI group—led by Director of National Intelligence Jay Clayton, along with Federal Trade Commission Chairman Andrew Ferguson, Office of Personnel Management chief Scott Kupor, and Emil Michael, the Pentagon’s chief technology officer—as an aggressive enforcer of existing federal statutes.
The fierce debate over how to mitigate emerging AI risks has accelerated rapidly following a spate of alarming cyber breaches, alongside a now-viral essay from Anthropic Chief Executive Officer Dario Amodei that warned of the technology’s catastrophic risks. Amodei and other prominent industry leaders have called for additional government regulation and coordinated industrywide efforts to help mitigate these hazards, prompting some notable pushback from other tech executives and policy officials.
In a display of unlikely political alliances, Nvidia Corp. CEO Jensen Huang and former FTC Chair Lina Khan have both argued for the robust use of existing laws to prevent the dire outcomes that safety advocates continually warn about. At the same time, Khan has strongly criticized the notion of having the tech industry police itself, calling self-regulation “a recipe for disaster” and indicating that there is ample room for future federal AI legislation.
For President Trump and his key allies, the persistent threats of legal action are aimed squarely at spurring developers like OpenAI and Anthropic into ensuring their advanced systems run safely without heavy-handed federal oversight. During a congressional hearing last month, Treasury Secretary Bessent flatly rejected the idea of writing new rules, as well as any notion that AI labs should be spared from liability exposure.
“The best way to guarantee safety is that the creators are liable for what they build and generate,” Bessent told lawmakers. Sacks has repeatedly used the phrase “mother of all product liability lawsuits” to describe the severe consequences he believes should await AI companies that fail to manufacture safe products.
The federal government has already taken tangible steps toward making that aggressive approach a reality. The Federal Trade Commission is currently scrutinizing OpenAI, Anthropic, and other top AI companies regarding product safety, following several high-profile cybersecurity incidents. These events include a notable swarm of autonomous OpenAI agents successfully breaching Hugging Face Inc., a prominent repository for open-source software.
The FTC probe sets the stage for officials to pressure companies making foundational AI models into more intense self-regulation. It effectively tees up a credible legal threat for the developers who signed the voluntary accord with Trump that recommended adopting outside safety auditing and tweaking corporate board structures to better handle long-term safety risks.
If the Department of Justice, as President Trump has publicly floated, moves to prosecute private companies for rogue AI hacks, many of those legal cases would heavily hinge on the Computer Fraud and Abuse Act, or CFAA. This decades-old federal law requires prosecutors to prove that a human plaintiff intended to hack a target system. That stringent standard will prove exceedingly difficult to meet in cases involving unintended or autonomous AI agent behavior.
“AI agents could engage in conduct that would be a tort or even a crime for a human, and yet no one could be liable under current law,” Gabriel Weil, a law professor at the University of Houston Law Center and senior fellow at the Institute for Law and AI, said during a recent New York City Council meeting. Weil added that traditional negligence and product liability legal arguments currently apply to such incidents, though those approaches also possess significant limitations.
During a Senate hearing, Paul Ohm, a Georgetown University law professor who is set to publish a textbook on AI law, noted that it might theoretically be possible for developers to be held liable under the FTC’s broad product liability authority. However, he warned that the CFAA currently requires direct human intent—something typically only attributed to human actors—meaning autonomous AI agents may currently be entirely off the hook.
Federal lawmakers are already trying to change that legal reality. Senator Josh Hawley, a Missouri Republican, and Senator Chris Murphy, a Connecticut Democrat, plan to introduce bipartisan legislation that would amend the CFAA to make AI developers both civilly and criminally liable for failing to impose reasonable safeguards on a model’s inherent hacking capabilities.
Existing law does allow victims of rogue AI incidents to pursue traditional tort liability lawsuits, but those legal avenues are inherently limited because they would likely require a plaintiff to show that AI companies failed to provide reasonable care—an intentionally abstract duty that major corporations would likely argue they successfully fulfilled. In addition, “tort law reaches its limit once the responsible company is bankrupt,” Weil noted, meaning it may not offer adequate protection against civilization-level systemic risks.
A California nonprofit is currently testing what kind of legal accountability is actually possible under existing state law with a lawsuit filed against OpenAI over the Hugging Face breach. The case seeks a court order barring the company’s AI agents from accessing third-party systems without explicit permission, while also seeking to prohibit OpenAI from continuing any unsafe AI development practices that pose a public risk.
“We haven’t seen how a court will answer the question, but the idea that technology manufacturers are going to somehow fully get away from being liable for harm that their tech causes or abets seems super far-fetched,” said Michael Pastor, the dean for tech law programs at New York Law School.
Meanwhile, Representative Lori Trahan, a Massachusetts Democrat, released a draft of legislation designed to erase some of that legal ambiguity by holding AI developers strictly responsible for harm, even if they exercised reasonable care when building an agent or model. Her proposed bill would also bar companies from using the defense that their AI agents lack human intent.
Without new legislation, it will likely take years for the courts to apply existing legal precedent to entirely novel AI scenarios, Pastor said. That leaves the door wide open for developers and corporate end users to quibble over who bears ultimate responsibility when the technology causes real-world harm, and there are clear signs that those opposing camps have already begun to form.
Sacks, whose venture capital portfolio includes startups that deploy AI models as end users, and Huang, who maintains greater pricing power over his computer chips when AI developers face heightened competitive pressure, are both advocating for maximum legal responsibility to fall squarely on the developers.
At the same time, major AI developers, including OpenAI CEO Sam Altman and Anthropic’s Amodei, have consistently pushed for mandatory pre-deployment testing regimes—a regulatory move that could potentially shift some operational responsibility onto a government testing apparatus alongside their own companies.
For now, the overarching legal underpinning for software-related liability remains underdeveloped compared to other industrial fields, observed Julia Powles, a professor at the UCLA School of Law. That structural lag is primarily because sustained, decades-long lobbying by the tech industry has historically sought to “ensure that software is regulated by contract—terms of service and end-user license agreements—instead of by tort, crime, and consumer protection.”
“The same tech actors that have created deep dependencies in digital infrastructure are now recklessly accelerating cybersecurity threats to that very infrastructure—and then disclaiming responsibility for the resulting chaos,” Powles said. “There’s precious little space for the public in all these debates because the whole chess board has been set up by industry.”








No comments yet. Be the first to join the conversation!