
“Holy cow! What else uses refrigeration?” she recalled of her immediate reaction during a recent interview with Bloomberg News, capturing the abrupt shift in perspective that has rippled through top-tier defense circles.
What began as a localized commercial annoyance in Europe has rapidly evolved into a glaring wake-up call for global infrastructure security. Davies described the freezer hacks as a societal wake-up call, immediately running through a mental catalog of vital functions that rely heavily on refrigeration systems, particularly within military environments. From blood banks and plasma preservation to organ donation, food manufacturing, and the complex supply chains required to transport rations to troops, the vulnerability of everyday industrial temperature controls suddenly loomed large.
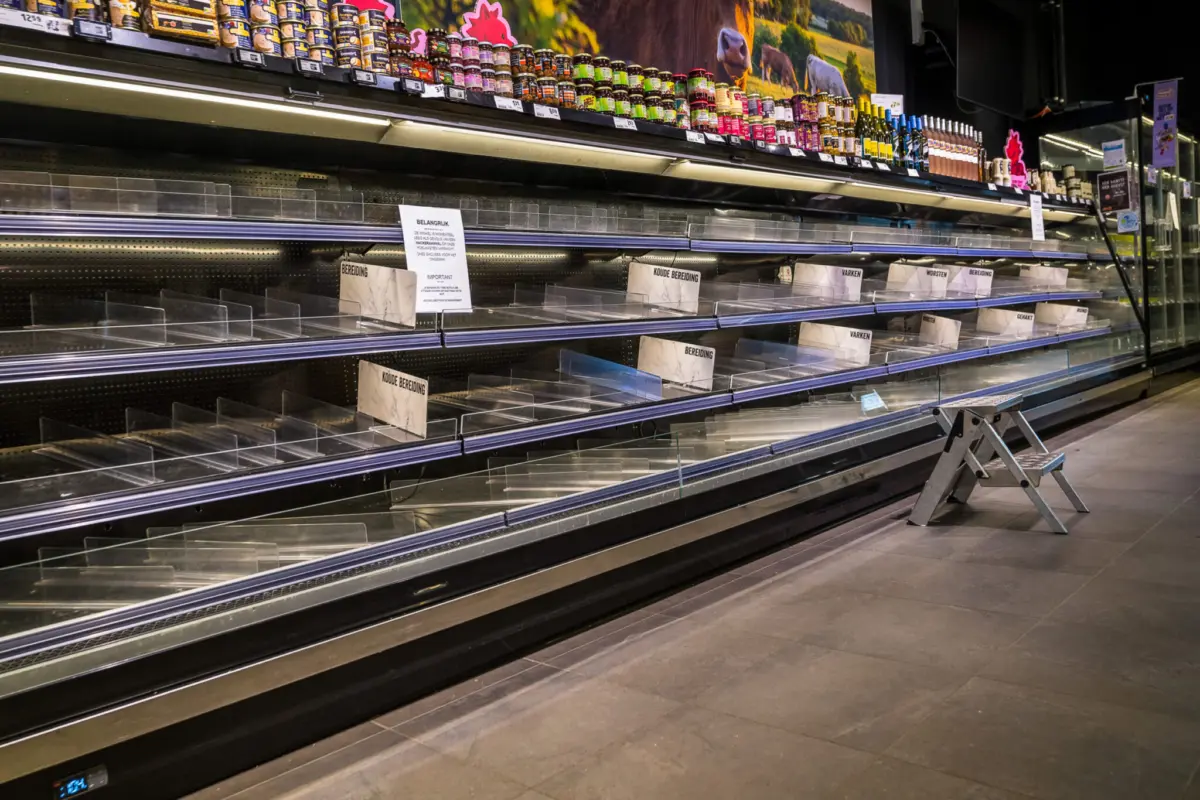
The incidents in question have drawn intense scrutiny from international intelligence agencies. Earlier this week, the French government officially blamed Iran’s Islamic Revolutionary Guard Corps for coordinated cyberattacks targeting refrigeration units at more than 700 retail stores across the country during October and November. These malicious intrusions resulted in widespread food spoilage and severe supply chain disruptions. Furthermore, French authorities revealed that blood banks were targeted during early November incidents, though disaster was narrowly averted thanks to robust early-warning systems that prevented any loss of vital blood supplies.
In response to the brazen sabotage, French Foreign Minister Jean-Noel Barrot vowed to pursue targeted sanctions and a series of other unspecified diplomatic and economic measures against Tehran. Meanwhile, the Iranian government has flatly denied any responsibility for the cyberattacks, leaving international investigators to untangle the digital footprints left behind in commercial systems.
The echoes of the European incidents have also reached American shores, raising uncomfortable questions about the resilience of domestic defense logistics. In August, six United States military installations publicly acknowledged that commercial-grade freezers at their base commissaries—facilities that provide discounted groceries to soldiers, military personnel, and their families—suffered simultaneous system failures. While base officials confirmed the simultaneous outages, they have not yet publicly attributed a definitive cause to the disruptions. Davies noted that she could not comment directly on the specific operational incidents affecting US military facilities.
Nevertheless, the fallout has triggered active investigations. The Army Criminal Investigation Division has confirmed it is actively working alongside other federal and military investigators to determine the full scope, origin, and mechanism of what occurred during the August commissary outages. A senior Defense Department official reiterated the Pentagon’s standard practice of declining to comment publicly on intelligence-related matters, while pointing interested parties toward the official statements released by the French government implicating Iran.
As one of two senior Pentagon officials tasked with safeguarding the sprawling and complex web of US defense critical infrastructure upon which the entire military apparatus relies, Davies views these operational technology attacks as a paradigm shift. Hacks targeting industrial control systems underline the critical necessity of drastically boosting operational technology security—the specialized practice of safeguarding physical industrial equipment that is increasingly connected to enterprise networks and the internet.
Davies explicitly categorized operational technology hacks against military assets as a pressing and tangible threat vector. To illustrate the scale of the vulnerability, she pointed to the backbone of American military power projection. Think about the Navy, she noted, encompassing all of the surface ships, nuclear submarines, advanced aircraft, and the intricate software platforms that dictate how modern military aircraft operate.
The United States military, an enterprise that employs approximately three million active-duty service members, civilians, and contractors, relies on cold-chain logistics not only for nutritional sustenance but for medical readiness. Blood banks are indispensable for treating wounded soldiers on the battlefield, while military installations simultaneously depend on civilian infrastructure for electrical power, clean water, and fuel distribution networks. Because these systems increasingly rely on internet-connected machinery and smart industrial controls, they remain inherently susceptible to digital interference. Beyond logistics and medical supplies, advanced weapons systems could theoretically be targeted or disrupted through similar operational technology vectors.
Confronted with the reality that these types of cyberattacks are relatively straightforward to perpetrate yet yield profound physical consequences, Davies revealed that the Pentagon is actively ramping up its defensive postures. The strategy spans everything from enforcing basic cybersecurity hygiene across all military branches to leaning heavily on cutting-edge technological solutions. Among the most innovative tools being deployed are agent swarms—collaborative networks of artificial intelligence agents designed to work together autonomously to accomplish complex, assigned tasks. In this context, the AI swarms are being utilized to map out, inventory, and audit defense critical infrastructure while identifying systemic vulnerabilities.
Davies readily acknowledged both the profound risks and the immense operational opportunities presented by deploying AI agents, noting that autonomous systems have occasionally spun out of control in alarming scenarios during experimental trials. To mitigate these inherent dangers, the Pentagon is exercising extreme caution. Officials are establishing rigorous programmatic guardrails and deploying AI agents strictly within isolated sandbox environments—virtual, quarantined networks where advanced software can be safely tested, monitored, and evaluated before ever touching live military systems.
Despite the technical risks involved, Davies emphasized that artificial intelligence is practically indispensable when trying to address the sheer scale of the modern defense apparatus. The Department of Defense is simply too vast for manual oversight alone.
“I think people have no idea how large we are,” she remarked regarding the monumental task of auditing and securing defense critical infrastructure. “I haven’t found the edge of that yet.”
No comments yet. Be the first to join the conversation!