
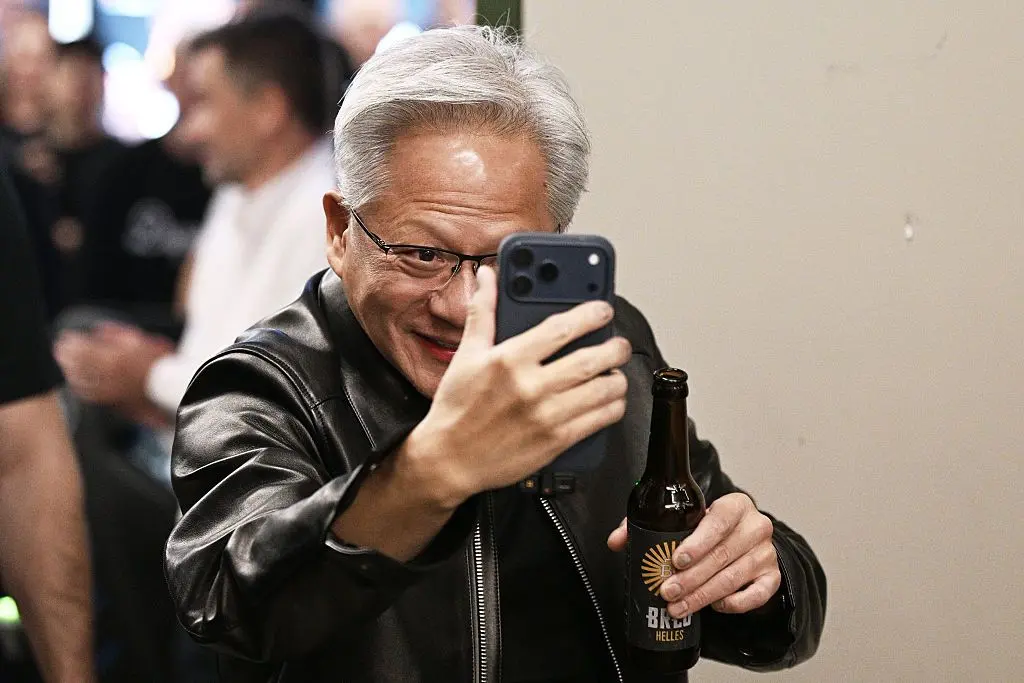
When Nvidia’s longtime chief security officer and head of product security stepped down quietly in late August, outsiders had little reason to suspect it signaled deeper turmoil within the semiconductor giant. Just two and a half months later, however, the departure of CEO Jensen Huang sent shockwaves through the tech industry. Huang’s exit followed a mounting cascade of questions surrounding his extramarital relationships. The scrutiny initially ignited over his connection to an executive at Megaspeed, a Singapore-based data center company currently facing U.S. federal investigations over suspicions that it has been funneling restricted Nvidia chips to China. The fallout subsequently widened as reports surfaced detailing two separate affairs between Huang and Nvidia employees.
At the time of his departure, David Reber, who spent four years as Nvidia’s chief security officer and seven years with the company overall, attributed his exit to personal health reasons. Writing on LinkedIn in late August, Reber told his professional network that the pivot was entirely unplanned. He explained that he needed to prioritize his family and his health, disclosing publicly for the first time that he had been diagnosed with young-onset Parkinson’s disease more than two years prior.
Reber was succeeded by Saša Zdjelar, a seasoned security executive who previously spent 17 years at ExxonMobil in Houston, where she departed as a senior IT manager. Following her tenure at the energy giant, Zdjelar spent a year at Salesforce and several years at the cybersecurity firm ReversingLabs. Reached for comment regarding the timing of the leadership transition and what the internal security team may have known about the surrounding controversies, Zdjelar did not respond.
To date, no public evidence directly connects the role changes of either Reber or Zdjelar to the escalating federal scrutiny surrounding Megaspeed. Nevertheless, industry observers and security specialists are left wondering what Nvidia’s corporate security apparatus understood about the government’s investigation into Megaspeed, what they knew regarding Huang’s relationships, and whether any internal alarms were ever raised. Reber declined to respond to inquiries regarding these matters, and Nvidia representatives have similarly declined to answer related questions.
Within the typical corporate hierarchy, relationships between a chief executive and subordinates fall under the purview of human resources, the legal department, and the board of directors rather than corporate security. Yet, security experts point out that any personal relationship—even one contained entirely within an office environment—can create critical vulnerabilities, giving foreign intelligence services leverage over high-ranking executives who are desperate to keep such details private. Furthermore, Huang’s relationship with an executive at Megaspeed, a firm already under active federal investigation, extended far beyond a standard workplace romance. (Megaspeed has consistently denied any wrongdoing.)
Despite the high stakes, detecting these vulnerabilities is an extraordinarily difficult task. Modern intelligence services rely heavily on human intelligence collection, gathering sensitive information through everyday conversations and social engineering rather than traditional digital hacking. According to retired senior intelligence officer Nicholas Eftimiades, who has trained more than 1,000 corporate security professionals, these subtle methodologies make it exceptionally challenging for standard corporate security teams to identify emerging risks before they manifest as crises.
It is clear that some individuals within Nvidia possessed fragments of the broader picture well before Huang’s departure. Nvidia’s top legal counsel was actively engaged with the United States government regarding the Megaspeed inquiry more than a year ago, as The New York Times reported earlier this week. (Nvidia has maintained that it routinely and cooperatively communicates with government officials.) Meanwhile, reports detailing Huang’s relationships with employees suggest that various colleagues were aware of the situations, even though such personal behavior is not expressly forbidden under Nvidia’s official code of conduct. The Times cited five Nvidia employees who stated that Huang was involved with a vice president who reported directly to him, while Reuters subsequently cited two sources detailing a second relationship. What remains entirely unclear is whether any of this intelligence ever successfully reached the corporate security team.
Even if information regarding the relationships or the federal inquiries had reached Nvidia’s security team, Eftimiades—author of the 2020 book Chinese Espionage Operations and Tactics—noted that corporate security divisions are frequently hamstrung by limited resources. Unlike business units that generate direct revenue, security departments are frequently viewed as cost centers and are notoriously underfunded. It is astonishingly common, Eftimiades said, for corporate chief executives to respond to proactive security warnings with a rigid directive of compliance-only spending, offering not a nickel more than what is legally required to check the bare minimum boxes.
Furthermore, industry specialists argue that many corporations define the scope of security far too narrowly. In a recent opinion piece published in The Hill, Don Aviv, CEO of the corporate investigations firm Interfor International, and author Jeremy Hurewitz criticized the broader corporate mindset. They wrote that too many companies still approach security primarily as a matter of protecting physical facilities, preventing routine cyberattacks, and responding to localized physical threats. The co-authors argued that modern enterprises must pay significantly greater attention to insider threats, including the systematic cultivation of executives and employees by foreign intelligence services, suspicious business relationships, conflicts of interest, and attempts to extract sensitive corporate information through trusted personal contacts.
Given Nvidia’s massive global scale, its critical technological assets, and its sensitive geopolitical partnerships, it would be surprising if its security team did not maintain a more expansive remit than most corporations. Yet, security analysts acknowledge that such blind spots remain entirely possible even among elite firms.
In fairness, security experts emphasize that certain vulnerabilities simply fall beyond the operational capacity of any corporate security team. Speaking generally rather than specifically about the Huang case, Eftimiades outlined a hypothetical scenario in which a chief executive complains during a meeting about being stymied by a board of directors that opposes a specific strategic move. To a trained intelligence asset listening in, that casual remark identifies precisely who the organizational obstacle is. The foreign intelligence service then asks who the sticking point is and actively searches for ways to infiltrate that person’s email and mobile communications.
What rival intelligence services are often hunting for is policy insight rather than raw source code or hardware specifications. They want to know who is pushing to alter export controls, who the primary internal blockers are, and how corporate strategies will shift. The intelligence world behaves much like cancer, Eftimiades explained, noting that once it breaches the body, it systematically seeks to spread and reach into vulnerable areas.
This playbook is far from new, Eftimiades added, noting that it is particularly prevalent in operations linked to China. Any corporate executive routinely dealing with the country will readily acknowledge that they have been approached by intelligence operatives. He pointed to numerous historical accounts of diplomats walking into foreign hotel rooms to find themselves compromised, noting that while the tactics mirror Cold War methodologies, modern operations differ because the relationships cultivated by foreign services now frequently span years rather than weeks.
Advanced technology can further augment traditional human intelligence operations. Eftimiades pointed to International Mobile Subscriber Identity (IMSI) catchers as a prime example. These devices mimic legitimate cellular towers, forcing nearby mobile phones to connect to them. A basic version of the hardware can cost approximately $1,000 and easily fit inside a suitcase, though government-grade variations command significantly higher prices. Such technology factored into a couple of prominent Chinese espionage cases investigated over the past year.
Experts note that it remains publicly unknown whether such specialized surveillance devices were deployed against Huang, whose personal mobile phone presumably featured high-level security hardening designed to detect compromises, even if it could not entirely prevent them. Ultimately, what Nvidia’s internal security team knew about these developments, and whether they possessed the capacity to act upon that knowledge, will only become clearer as the board of directors’ independent investigation and parallel federal inquiries continue to unfold.
In the meantime, Eftimiades expressed hope that the high-profile episode serves as a vital wake-up call for American industry at large, which he characterizes as mostly clueless regarding the sophisticated tactics employed by foreign intelligence services. Estimating that the United States has lost trillions of dollars in intellectual property over the years, he concluded that whatever defensive measures corporate America currently believes it is taking are simply not working.
No comments yet. Be the first to join the conversation!